CVE Bestiary
Recent AI models are revealing a host of bugs ("Common Vulnerabilities and Exposures") in widely used software.
Personally, I find such reports to be dry reading, so I've converted a number of recent reports into Magic-style cards. Should I make more? Let me know.
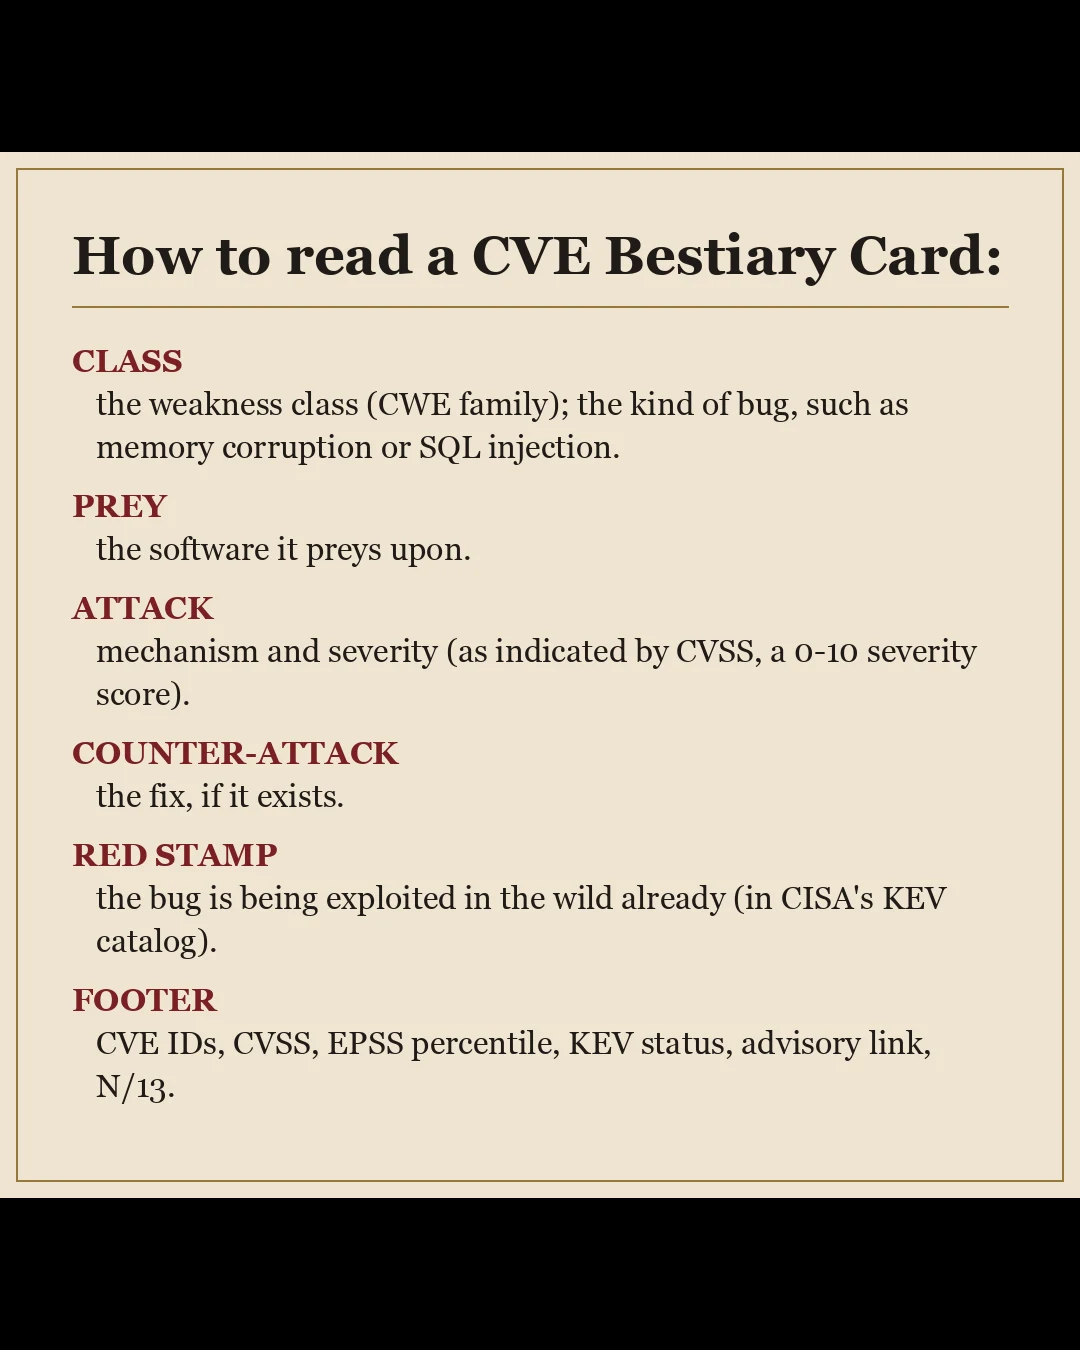
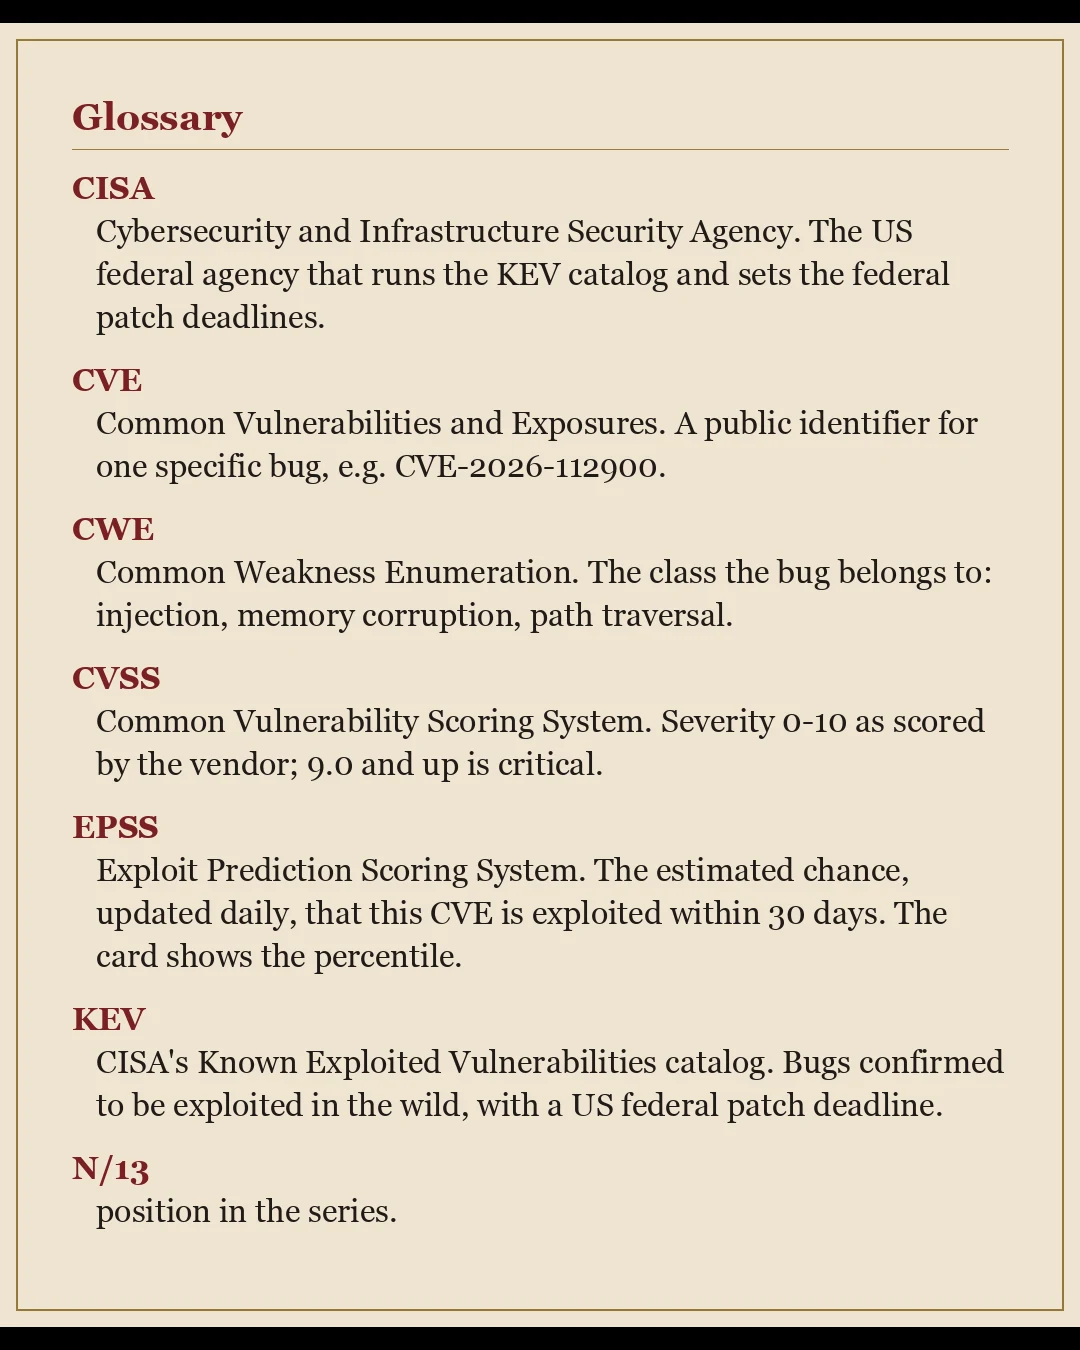
Each card is a specimen page for one advisory: the weakness class, what it preys on, how it attacks, the fix, and the scores. Cards marked (provisional) were built from the vendor advisory before NVD carried the record, and their copy comes from the advisory named on the card.
16 cards, CVSS 10.0 highest, 7 in CISA KEV, 4 provisional
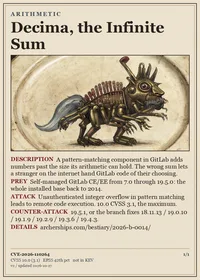
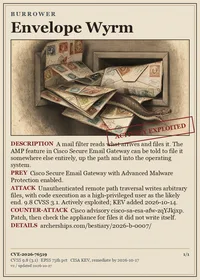
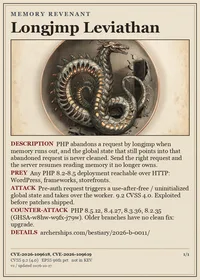
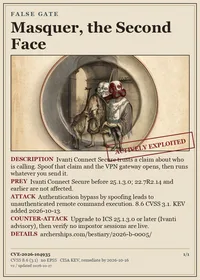
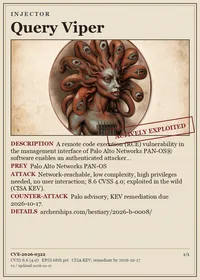
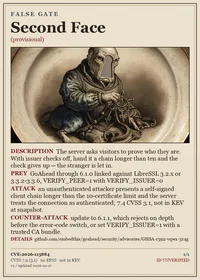
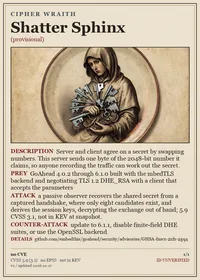
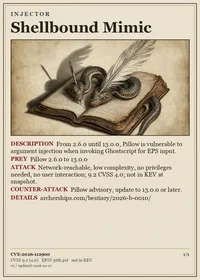
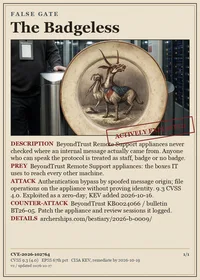
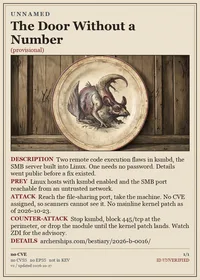
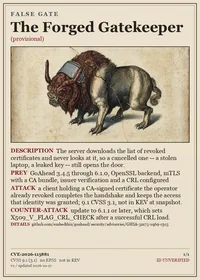
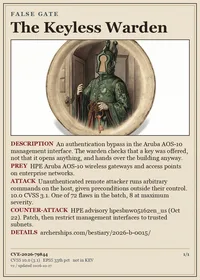
Scores are the CVSS base scores the card records; dates are the advisory publication dates.